- The External User Authentication Requirements must be met as part of this procedure.
- It is recommended that the set up of your Azure account and application be performed twice:
- Azure staging > Vindicia Subscribe Staging
- Azure Production > Vindicia Subscribe Production
-
Register a new App as follows:
- Log in to your Azure account and navigate to Azure Active Directory > App registrations.
-
Create a new application by selecting + New registration.
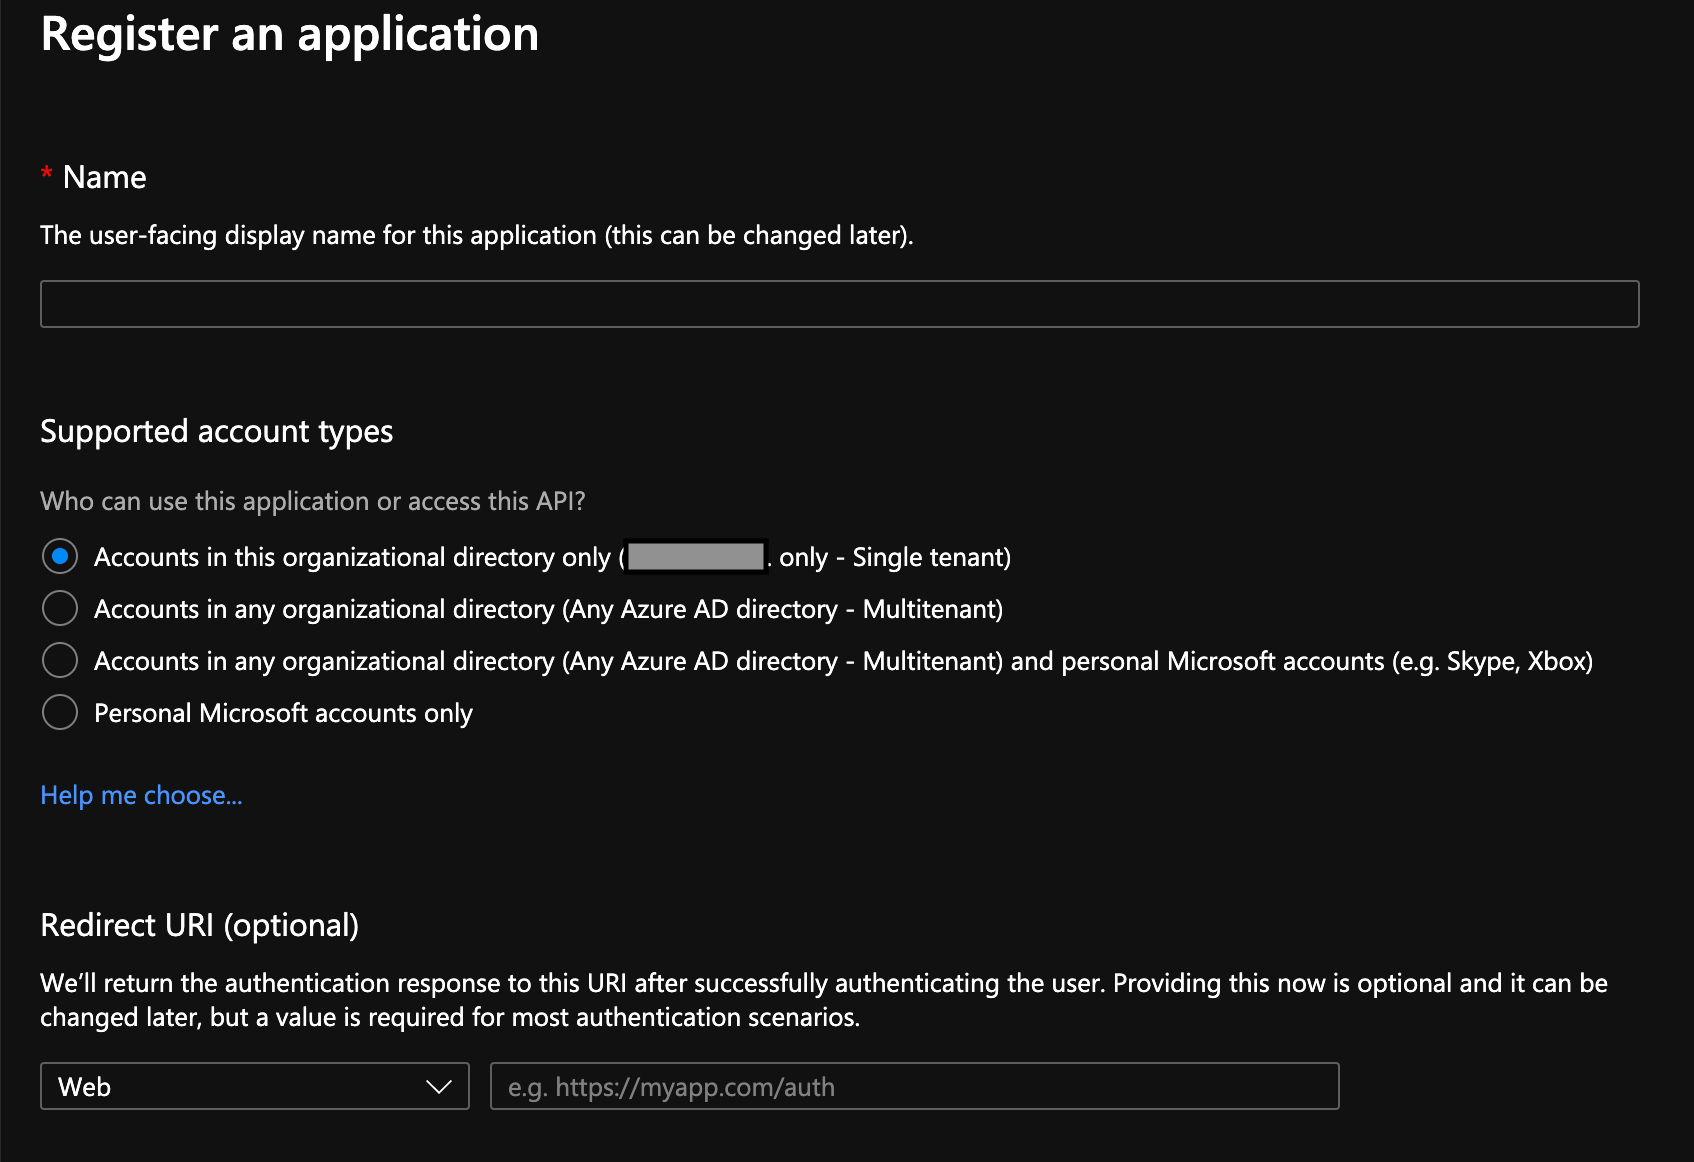
- Enter a Name.
- Select a Supported account types option. Consult your security organization and the Azure documentation. Record this choice because your OIDC Discovery Metadata URL depends on this choice.
- Leave the Redirect URI (optional) field blank. You’ll provide this information later.
- Click Register. The application configuration Overview page appears.
-
Generate a Relying Party OAuth Client Secret on the Overview page as follows:
- Click Certificates & secrets. The Certificates and Secrets page appears.
- Click + New client secret. The Add a client secret panel appears
- Provide a Description and an Expires length that follows your security organization’s guidelines in the Add a client secret panel.
- Click Add.
- Copy the Value corresponding to the newly-created client secret into a .txt file. This is the Relying Party OAuth Client Secret that you will configure with Vindicia later. Note: Any changes made to the Client Secret value must be communicated with Vindicia Client Technical Support.
-
Configure the Redirect URIs as follows:
- Click the Overview tab.
-
Click Add a Redirect URI.
The Authentication page appears.
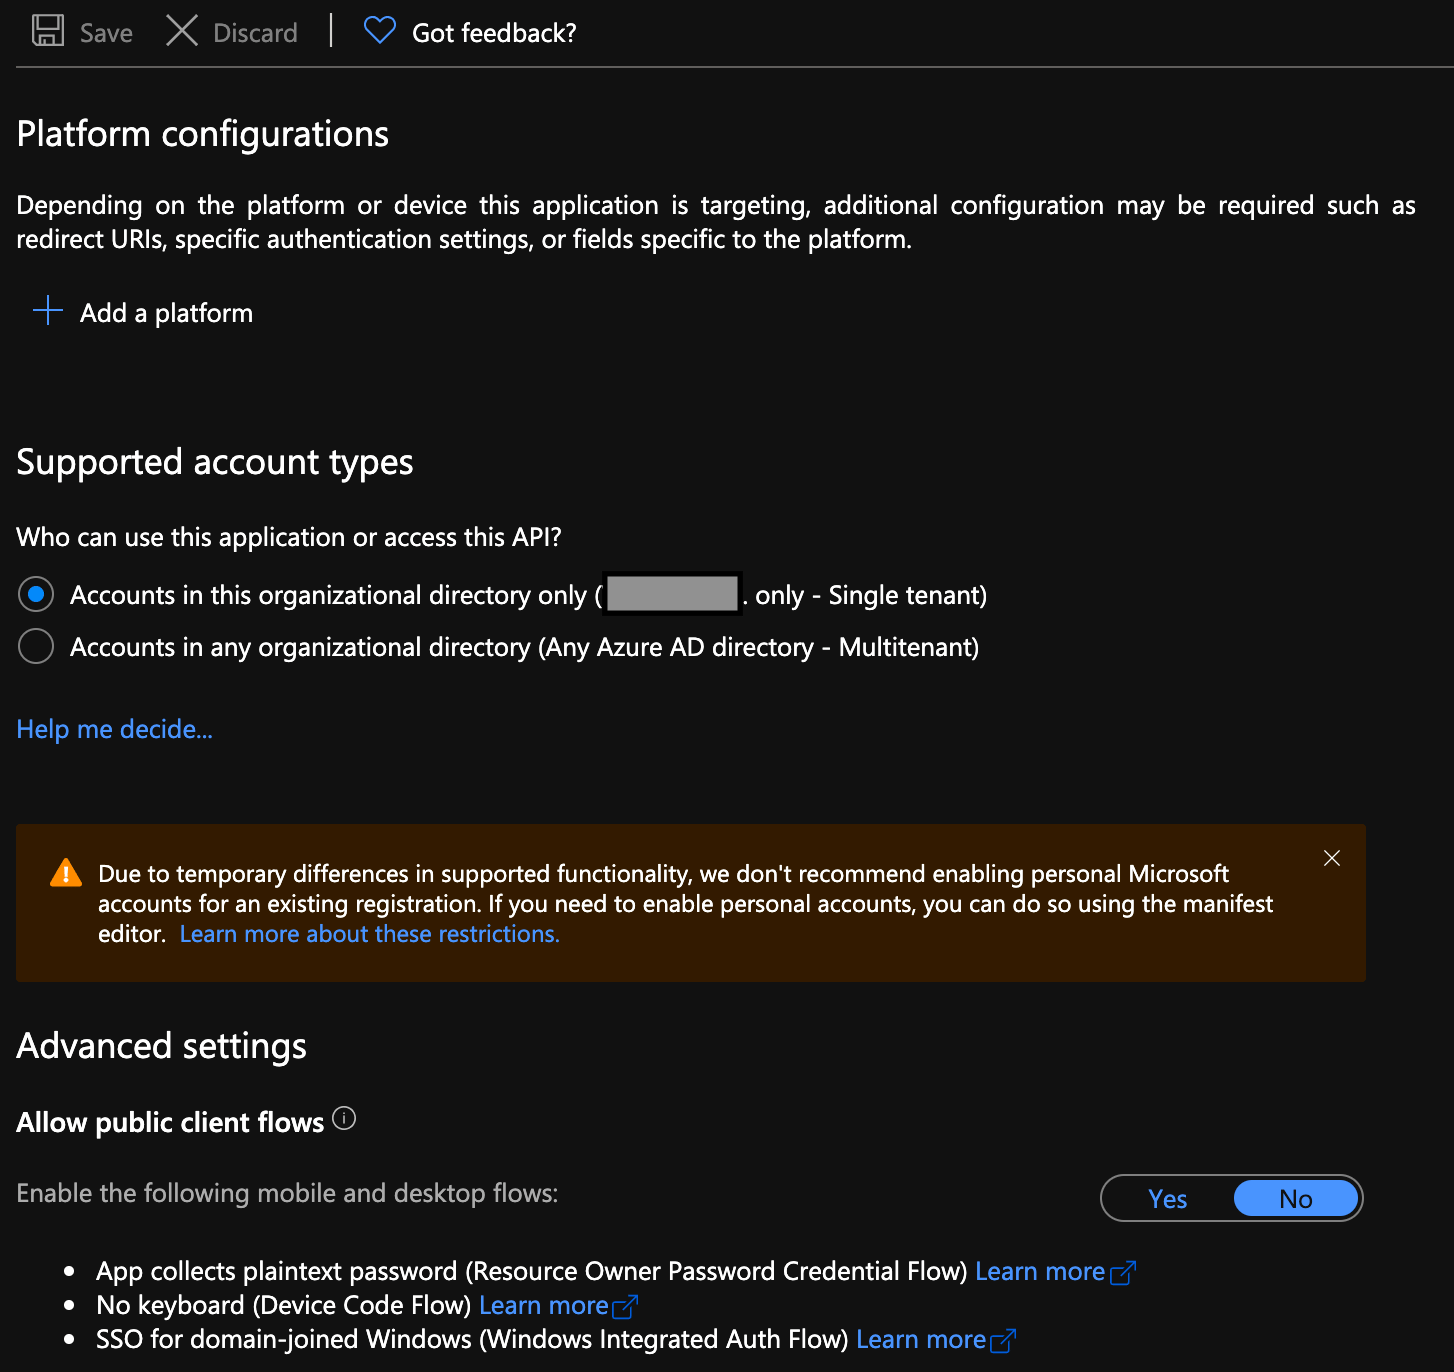
- Click Add a platform under Platform Configurations. The Configure platforms panel appears.
- Click Web in the Configure platforms panel.
-
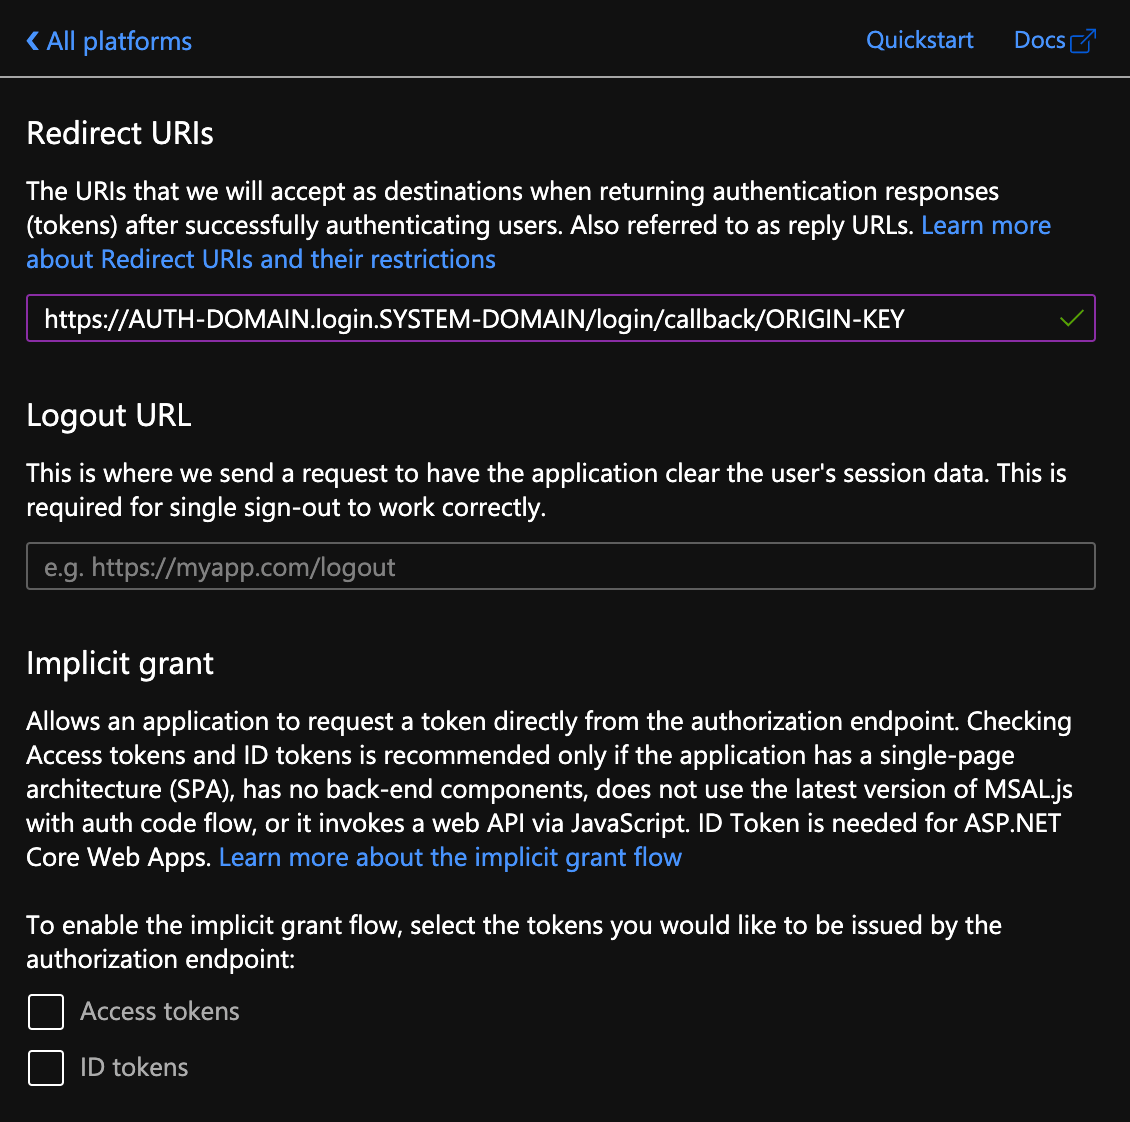
Under Redirect URIs, enter the following as relevant for either your production or staging implementation:
- Staging:
- Vindicia Merchant Portal staging: https://portal.staging.us-west.vindicia.com/portal/sso_return
- Production:
- Vindicia Merchant Portal production: https://portal.vindicia.com/portal/sso_return Note: Once you add a URI, click Add URI to add any additional URIs.
- Staging:
- Leave the Logout URL field blank.
- Click the Access Tokens and ID Tokens check boxes in the Implicit grant section.
-
Click Configure.
- Return to the Overview page.
- Click Endpoints in the top panel.
- Copy the OpenID Connect metadata document to the .txt file.
- Return to the Overview page.
-
Copy the following values to the .txt file.
- Application (client) ID
- Directory (tenant) ID
-
Ensure the .txt file contains the following information:
- Application (client) ID
- Directory (tenant) ID
- Client Secret
- OpenID Connect metadata document
- Encrypt the .txt file and pass it to your Vindicia contact point for integration.
- Add the users that will use Vindicia Merchant Portal to the newly created application in Azure AD.